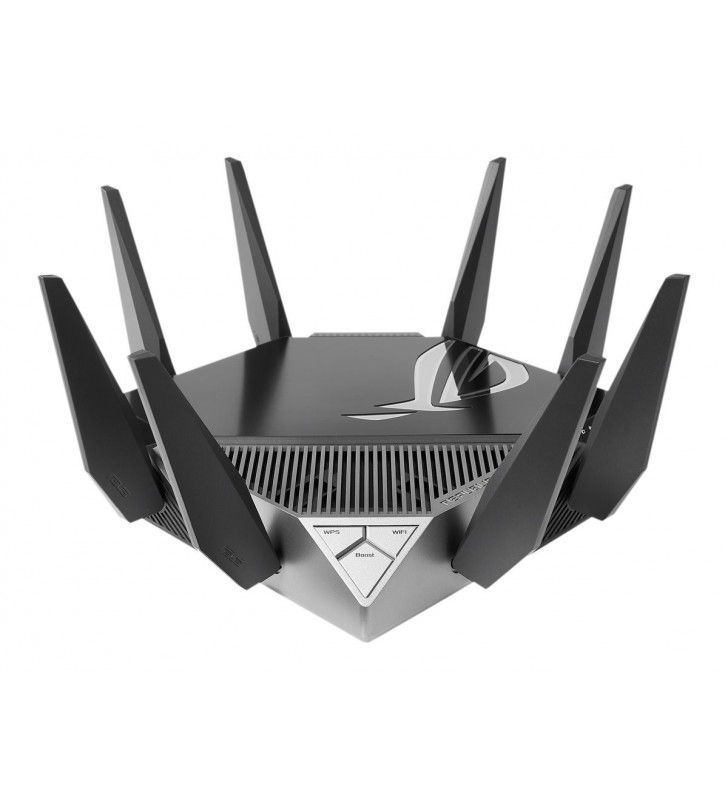
Asus released an emergency firmware update for its Wi-Fi 7 router lineup to patch an improper authentication flaw that grants unauthenticated attackers full administrative control.
Published in an Asus security bulletin on October 22, 2026, and updated on October 23, 2026, the advisory covers models running the Asuswrt 3.0.0.6_102 firmware branch, TechPowerUp reported. The primary improper authentication flaw, tracked as CVE-2026-75775, carries a CVSS v4.0 score of 7.7. According to Asus, an attacker connected to an adjacent network can exploit the bug to bypass login checks and take over the management interface without credentials.
The October 2026 bulletin for the 3.0.0.6_102 branch also addresses two additional high-severity flaws, Notebookcheck reported. CVE-2026-75779, rated at 8.6 on the CVSS v4.0 scale, requires user interaction to trigger but demands no prior privileges. The most severe of the trio, CVE-2026-93489, carries a CVSS v4.0 rating of 8.7 and allows an unauthenticated attacker on an adjacent network segment to compromise the router without any user interaction.
Because the adjacent-network vector requires proximity to the local subnet or wireless coverage area rather than wide-area internet reachability, the immediate exposure is narrower than a WAN-side remote code execution bug. Even so, an authentication bypass on a primary gateway exposes connected clients, DNS settings, and traffic routing rules to manipulation.
Asus did not publish an itemized list of affected hardware models or exact patched build numbers inside the public bulletin, identifying impacted devices strictly by the 3.0.0.6_102 firmware designation. That firmware branch powers the company's current Wi-Fi 7 portfolio. Owners can pull the patched release directly through the built-in web administration portal or download the image manually from the Asus support page for their specific model.
For administrators who cannot flash the new 3.0.0.6_102 build immediately, Asus outlined several interim countermeasures to shrink the attack surface. The company advises disabling remote management access from the WAN, restricting the web interface to known local machines, and setting distinct administrator and Wi-Fi passwords of at least 10 characters combining uppercase letters, numbers, and symbols. Administrators should also audit connected client tables to block unfamiliar devices, terminate unrecognized mobile companion-app sessions, and execute a full system reboot once the firmware installation completes.